This guide explains how Cloudpay IE fits into payroll and business payments for organizations operating through Irish channels. It provides objective background on the Cloudpay model, what stakeholders typically evaluate in pricing and supplier terms, and the operational conditions that affect onboarding. It also includes a comparison table, a step-by-step guide, and FAQs to help you plan responsibly.
If you’re assessing Cloudpay IE for payroll-related payments or broader business payment workflows in Ireland, the priority is not just the headline proposition—it’s how pricing, supplier responsibilities, service governance, and implementation requirements align with your operating model. Practically, you should confirm settlement timing, data-handling expectations, operational controls, and contractual conditions before you commit.
Below, the discussion stays focused on decision-relevant factors an industry professional would typically validate: payment lifecycle transparency, onboarding prerequisites, and how Cloudpay IE-supported processes integrate with your internal finance and HR operations.
Cloudpay IE is commonly referenced in the market as a service concept linked to payroll and employer payment workflows for organizations operating with Irish considerations. In very buyer evaluations, the “Cloudpay” name indicates a platform or service layer intended to streamline how employers handle payment obligations and related administrative steps.
Because “Cloudpay IE” is used as a shorthand in various conversations, buyers generally interpret it as one of these: (1) a payment facilitation offering connected to payroll operations, (2) a platform-driven approach to employer payment administration, or (3) a provider model that coordinates payment steps on the employer’s behalf. Your due diligence should clarify which of these interpretations applies to the exact offering you are considering.
From an objective standpoint, any payroll or payment-adjacent provider typically becomes embedded in three areas: data exchange, payment execution, and compliance operations. Each area brings requirements that affect cost, timeline, and control.
To evaluate effectively, you should not assume that all payroll-adjacent systems work the same way. Some solutions mainly improve the workflow interface for HR and Finance teams; others operate as a “payment layer” where certain actions are triggered by provider-side rules. The difference matters because it influences who is accountable when something fails—especially at payroll cut-off time.
In Ireland, where payroll and employer payment processes are often governed by internal controls, tax and reporting expectations, and bank-calendar realities, the provider’s execution and reconciliation approach becomes a core part of your risk profile. Therefore, you need to understand not only what the solution does, but also where the boundaries sit between your organization’s responsibilities and those of the supplier.
It’s also worth noting that “Cloudpay IE” may be mentioned alongside other terms—such as payout processing, employer payment workflows, beneficiary management, or reconciliation services. Your due diligence should require the provider to explain the end-to-end flow in plain language and then map each step to a system state, a record, and a responsible party.
When people ask about Cloudpay IE price information, they often expect a single figure. In practice, payment and payroll-adjacent services usually involve a combination of:
Rather than relying on informal quotes, the responsible approach is to request a written fee schedule and confirm what is included in the scope. Industry top practice is to map the provider’s work to your expected payment cadence and reporting needs, then verify how the pricing changes when the volume scales.
In many evaluations, buyers discover that “price information” is ambiguous because the supplier uses multiple pricing dimensions. For instance, pricing might depend on:
Therefore, treat “price” as a structured commercial model, not a single number. You should ask the supplier to provide:
You should also validate your forecast. If your organization plans for headcount growth, multi-entity structures, or new regions later, confirm whether your pricing structure is stable or subject to renegotiation. Buyers often accept pricing that fits today’s payroll volume but causes friction after a merger or expansion.
Finally, insist on a scope statement that ties price to responsibilities. If pricing is low but reporting is limited, the real cost may shift to your internal teams who do manual reconciliation or additional data cleansing. Conversely, a higher subscription may reduce operational burden. You can only judge value by linking commercial terms to operational outcomes.
Another crucial step in evaluating Cloudpay IE is identifying the supplier responsibilities relative to yours. Buyers often underestimate this step and later encounter operational friction.
For objective clarity, you should ask how the supplier handles:
This “responsibility mapping” is especially important when multiple internal teams interact—HR for pay inputs, Finance for accounting treatment, and Operations for approvals.
Responsibility mapping becomes more complex when you introduce multiple workflows such as:
In each scenario, the supplier must clearly state what they do and what you do. For example, if employee bank details change close to cut-off, who is responsible for ensuring the updated details are valid and accepted?
To make this actionable, use a simple RACI approach (Responsible, Accountable, Consulted, Informed). You can create a grid with rows representing end-to-end steps (data ingestion, validation, approval, execution, confirmation, reconciliation) and columns representing internal and supplier parties. The output should explicitly confirm that there are no “gaps” where nobody owns a step during critical windows.
Also validate contractual language: who is liable when a payment is delayed due to supplier-side processing, versus a payment is incorrect due to customer-provided data? When you align responsibility mapping to contractual terms, you reduce the chance of dispute during incidents.
Moreover, supplier responsibilities should extend beyond the “happy path.” Ask how they behave when:
A provider’s answers to these questions often reveal maturity level: whether they have a repeatable process and whether they provide adequate evidence to support audit requirements.
Very payment and payroll-adjacent services—whatever the brand—place conditions/requirements on customers to maintain reliability and auditability. In typical implementations, these can include:
Even if your onboarding team is technically ready, governance readiness is often what determines timelines.
In practice, you should expect the supplier to require disciplined internal preparation, such as:
Operational requirements are not purely administrative. For example, approval workflow design impacts operational speed and error recovery. If approvals are too restrictive, payroll cut-offs may be missed; if too permissive, control weaknesses may emerge.
Also consider how the supplier expects you to manage data changes. Some providers require that beneficiary bank details are updated only during specific windows, or they require additional verification steps when data changes rapidly. Ask about these rules and document them internally.
It’s also common that the supplier will request proof of governance maturity—such as policies for access management and segregation of duties. If your organization is not prepared, you may face delays that are not obvious from initial commercial discussions.
Finally, you should clarify what “go-live” means. Is it when integration is connected? When the first test run passes? When you successfully execute a real payroll run? A precise go-live definition is crucial because it dictates whether incidents during early cycles are treated as onboarding learning or as production issues.
From an industry expert’s point of view, the decisive factors are those that reduce risk and improve predictability:
When those points are strong, the operational benefits usually materialize: fewer last-minute corrections, faster reconciliation, and clearer ownership across stakeholders.
However, “transparency” can mean different things depending on the provider. You should ask for concrete examples of how they present payment lifecycle states. For instance:
Additionally, exception handling should be evaluated in the context of operational time pressure. Payroll cycles are time-bound. Ask how quickly the provider surfaces errors. Also ask whether the supplier provides guidance for remediating errors without requiring repeated vendor intervention.
Audit trail quality is also not just about “having logs.” It’s about whether logs include sufficient evidence and context. You should evaluate what’s captured, such as:
Operational resilience should include not only technical reliability but also process reliability. A mature provider will have a cut-off calendar, a defined approach to banking disruptions, and an escalation tree. It should also clarify communication expectations: what you are notified about, by whom, and when.
Integration maturity should be validated with realistic payroll data structures. Even if API documentation exists, field mappings can still break due to differences in naming conventions, data types, or formatting (for example, sorting of bank account details). You should insist on a test plan that covers:
Finally, provider-led workflows should support your operational model. If your internal processes depend on specific sign-offs, time windows, or reporting outputs, confirm the provider’s workflow can accommodate them without excessive manual steps.
For organizations evaluating Cloudpay IE, “nearby” contexts typically mean you’re considering suppliers, teams, or operating touchpoints within the practical radius of Irish operations—whether that’s support coverage, onboarding coordination, or the timing of payroll processes relative to local banking calendars. In Ireland, businesses commonly align processes around local banking days, payroll calendars, and internal governance expectations tied to UK/EU-like documentation standards.
In practical terms: confirm how settlement timelines behave around Irish bank holidays and whether reporting conventions match your internal accounting expectations.
Localization also extends beyond calendars. For example, you should consider:
Another localization dimension is how the supplier communicates incidents and operational status. Irish payroll and finance teams may need guidance tailored to local execution patterns. Ask whether the supplier has experience supporting Irish organizations with similar payroll cadence and internal controls.
Also ask about “what if” scenarios relevant to Ireland—such as bank holiday effects, end-of-month processing, or disruptions in banking channels. The goal is to understand whether the supplier simply documents general assumptions or has a specific operational playbook.
If the provider’s documentation is generic, you may face uncertainty during critical periods. You can mitigate this by requesting an Ireland-specific cut-off calendar, incident response approach, and sample reporting formats used in Irish contexts.
| Evaluation Area | What to Compare for Cloudpay IE | Typical Source to Request | Conditions / Requirements to Verify |
|---|---|---|---|
| Pricing structure | Setup costs, recurring fees, transaction or run-based pricing, and included services | Written fee schedule; statement of scope | Confirm pricing triggers (e.g., number of employees, payment runs, add-ons) |
| Supplier responsibility | Who validates data, who initiates payments, who handles exceptions and rework | Operational responsibility matrix; service description | Define escalation paths and approval roles; clarify turnaround times |
| Onboarding readiness | Timeline, required inputs, test cycles, and go-live criteria | Implementation plan; onboarding checklist | Confirm HR/payroll data formats, required fields, and cut-off alignment |
| Reconciliation and reporting | Granularity of reports, reconciliation workflow, and audit trail structure | Sample reports; reporting guide | Ensure reporting meets internal audit needs; confirm retention expectations |
| Security and governance | Access controls, role-based permissions, and approval workflows | Security documentation; governance overview | Confirm separation of duties; validate user provisioning processes |
| Settlement and timing | Payment cut-off times, bank calendar handling, and confirmation cadence | Service-level description; cut-off calendar notes | Verify what happens on non-standard banking days |
The following guide is designed to be actionable while staying objective. You can use it whether you’re evaluating Cloudpay IE for a small team or a larger organization with multiple stakeholders.
Most evaluations stop at onboarding and high-level reporting, but payroll-adjacent payment workflows have recurring operational touchpoints. To make your evaluation robust, expand your due diligence to include how the solution behaves repeatedly across monthly cycles, what happens when errors occur, and how governance is maintained over time.
For example, you should confirm how the solution handles:
In mature operating models, these concerns are addressed with structured controls and evidence. A provider may demonstrate an excellent one-time test run, but your risk profile depends on repeated cycles and the consistency of error handling.
Therefore, ask for a demonstration that includes at least one “non-happy path” scenario. Good examples include:
Request sample outputs for these scenarios and evaluate whether the error messages are actionable. You should also check whether the supplier provides enough data for you to correct entries without having to contact them repeatedly.
Additionally, consider how the solution interacts with your internal systems. If HR exports payments to Finance, determine whether the process uses manual file transfer, scheduled exports, or API-based workflows. Each method has different failure modes and controls:
To keep your evaluation practical, list your current workflows and determine where the provider solution plugs in. Then determine what you need to modify internally, such as:
By documenting your “current process” and “target process” you can better estimate adoption effort and operational risk.
Security and governance are commonly discussed as high-level assurances, but what you need for payroll operations is evidence that access controls, segregation of duties, and audit capabilities work in practice.
When evaluating Cloudpay IE, ask for details about:
In a payroll context, segregation of duties is not optional. If the same users can submit payments and approve them, your control environment weakens. Even if the provider enforces internal controls, your organization still needs to implement governance that aligns with its risk appetite and internal audit expectations.
Also validate who can do what during cut-off. Payroll cut-off times are short. If governance is too rigid, it may cause delays. Conversely, if governance is too loose, auditability and control may suffer. The best approach is to align provider workflow states with your internal control policy.
Another governance check involves external access. If you have multiple internal teams, ensure that the supplier solution does not create excessive shared accounts or overly broad permissions. Shared accounts can undermine audit trails and accountability.
Finally, ask for evidence of operational security practices: incident response, vulnerability management processes, and general security posture. You may not need every technical artifact, but you should confirm that there is a consistent security program behind the service.
Reconciliation is often where payroll-adjacent payment workflows either succeed operationally or fail quietly. You should evaluate whether the provider’s reporting makes reconciliation efficient and reliable.
When comparing Cloudpay IE reporting, focus on:
In many organizations, reconciliation includes multiple steps:
You should validate whether the provider supports each step. For example, if the provider’s reconciliation output only provides a summary but your internal process needs detail, you may face manual work or the need to pull additional data from bank statements.
Also request sample reports, not just descriptions. Review:
Consider retention as well. Payroll-related payment evidence may be subject to internal retention policies. Confirm how long the supplier retains records and whether you can export them.
Audit trail structure also matters. A good audit trail allows you to answer: “What happened, when, and who approved it?” If the provider provides logs without clear mapping to your internal record sets, reconciliation will be more complex.
Finally, evaluate whether the provider provides a reporting guide or data dictionary. A structured guide helps your Finance and IT teams implement consistent reconciliation routines.
Settlement timing is often where operational expectations diverge from contractual assumptions. Therefore, you need to understand how Cloudpay IE handles cut-offs, banking days, confirmation cadence, and reconciliation timelines.
When evaluating timing, confirm:
Because Ireland’s banking calendar affects operational timing, you should request an Ireland-specific cut-off calendar and clarify behavior around public holidays.
You should also validate contingency procedures. For example, if a payroll run fails due to a system issue near cut-off, what is the recommended remediation path? Can you resubmit data? How do you avoid duplicate payments?
In addition, determine whether the provider offers controls to prevent duplicate submissions. For example, if you resend a file due to an integration timeout, you need to know how the provider detects duplicates or how you can confirm idempotency.
Timing also affects your payroll communications to employees. If employee payment dates or expected processing windows are influenced by the provider’s execution timing, you should align internal expectations early.
Therefore, validate what the provider can guarantee (and what they cannot). Many providers use service-level descriptions; ensure you understand what those descriptions mean practically for your operations.
Even if a supplier claims integration “works,” operational fit depends on data mapping quality and how edge cases are handled. Integration due diligence should not be treated as a purely technical project. In payroll workflows, integration touches governance and reconciliation.
When assessing Cloudpay IE integration, confirm:
You should also validate data quality responsibilities. For instance, if the HR team provides a bank account with whitespace or formatting differences, does the provider normalize the data, reject it, or accept it incorrectly? Ask about specific validation approaches.
Integration also affects your internal data governance. If you rely on HR systems that may change field names or export structures, confirm how those changes are managed. A provider solution that is resilient to format variations reduces operational risk.
Another practical integration check is how the solution handles multiple entities or business units. If you operate across multiple payroll entities, ensure the provider supports that structure and does not collapse records in ways that complicate reconciliation.
Finally, integration maturity includes documentation. Ask for a data dictionary and any sample payloads used for testing. Also request guidance on how to test in a staging environment and whether you can validate end-to-end workflows prior to go-live.
Onboarding timelines are often presented as ranges, but decision-quality diligence requires clarity on what must happen before go-live. You should insist on a structured implementation plan for Cloudpay IE evaluation.
At minimum, your plan should include:
Go-live criteria should not simply be “integration connected.” Instead, it should include measurable outcomes such as:
To maintain control, include acceptance criteria in the implementation plan. This helps prevent ambiguity during early cycles after go-live.
Also validate the provider’s role in training. Ensure HR, Finance, and Operations understand what they must do, what reports to use, and how to interpret exceptions.
Implementation can stall when responsibilities are unclear. For example, if the provider expects the customer to provide specific data formats but the customer assumes the provider will map fields automatically, the project may face delays. That’s why responsibility mapping should be completed early and then reinforced through documentation.
Finally, confirm how changes are managed post go-live. If you intend to add new entities, increase employee counts, or introduce new integration methods, confirm how change requests are handled and whether they require new testing cycles.
Even when the provider’s solution is strong, the project can fail if the internal operational model is not aligned. Therefore, you should evaluate how the workflow changes day-to-day.
Consider the roles that will be involved:
Evaluate whether Cloudpay IE-supported workflow maps cleanly to these roles. For example:
Also evaluate workload. A provider might reduce some steps but introduce new tasks such as monitoring dashboards, exporting reports, or managing reconciliation evidence. Determine whether these tasks are manageable and whether they fit into existing team capacity.
Operational fit includes communication processes. During payroll cut-offs, issues can arise quickly. Confirm how the supplier communicates problems and how quickly. Also confirm whether you have access to relevant logs or status pages.
Finally, you should consider training and documentation quality. If the solution is difficult to interpret, operational teams may develop workarounds that undermine governance and auditability.
To evaluate Cloudpay IE comprehensively, build a risk register that covers operational, data, security, and contractual risks. This risk register should not be a theoretical exercise. It should directly inform your acceptance criteria and your incident playbook.
Example risk categories include:
For each risk, specify:
This approach ensures you evaluate Cloudpay IE not only on features but on operational reliability.
Also plan for post go-live monitoring. The first few payment cycles are usually critical. Define what you will measure—such as number of exceptions, time to resolve issues, reconciliation turnaround time—and set a remediation plan if targets are missed.
Pricing and scope are commercial topics, but in payment workflows, contracts also determine operational flexibility. During evaluation, confirm that contractual conditions do not conflict with your operational reality.
When reviewing Cloudpay IE contract terms, pay special attention to:
Many buyers focus only on cost and overlook exit and transition terms. Yet for payment workflows, you need to ensure you can retrieve records quickly and continue payroll operations without unacceptable downtime.
Therefore, ask about:
Also ensure that pricing does not create perverse incentives. For example, if pricing discourages additional reports or specific exception handling, your operational team might avoid using those features, which increases risk. Clarify whether essential operational capabilities are included or separately charged.
Beyond calendars, localization includes documentation style, support expectations, and operational rhythm. In Ireland, payroll and Finance teams often work with tightly controlled internal processes and audit routines. Therefore, you should evaluate whether Cloudpay IE materials match those routines.
Ask for:
Also evaluate language and clarity. If documentation uses ambiguous terminology or lacks examples, your internal teams may interpret controls incorrectly.
Support coverage should align with when payroll teams work hardest. If escalation is only available at certain hours, confirm whether that aligns with your cut-off windows.
Where possible, request references or evidence from similar Irish organizations. If the supplier can’t discuss comparable deployments, that may not be a deal-breaker, but it increases diligence requirements around tests and onboarding readiness.
In typical market usage, Cloudpay IE refers to a provider or service model connected to payroll and payment workflows for organizations operating with Irish considerations. Your supplier documentation should specify whether the scope includes payment execution, administrative steps, reconciliation support, or a combination.
Interpret Cloudpay IE price information as a structured fee schedule rather than a single number. Ask for what’s included (onboarding, reporting, support), what varies (employee count, payment runs, integrations), and any conditions that affect total cost.
The “supplier” is the organization providing the service referenced as Cloudpay IE. You should identify the exact legal entity in the contract and confirm how responsibilities are split between you and the supplier (data validation, payment initiation, exception handling, and reporting).
Onboarding commonly depends on data readiness, governance setup (roles and approvals), integration requirements, and alignment to payment cut-off schedules. You should request a written checklist and implementation plan.
Yes. Operational risks can include data mismatches, reconciliation delays, and approval or cut-off misalignment. Mitigation typically comes from a structured test run, clear responsibility mapping, and an onboarding plan with measurable go-live criteria.
Request sample reports and confirm the level of detail needed for reconciliation and internal audit. Ask whether reports include payment lifecycle states, error notes, and the fields required to support your accounting processes.
Often it can, but integration capability depends on the offering and your current HR/payroll system. Ask about supported data formats, integration options (manual import, export workflows, APIs), and expected effort for mapping fields.
Confirm cut-off times, confirmation cadence, and how the provider handles non-standard banking days. Also clarify the reconciliation timeline after payment execution.
Ask for evidence such as test payment lifecycle states, validation results, reconciliation outputs, audit logs for approvals, and confirmation messages. Ensure you can demonstrate that Finance can reconcile using the outputs without manual vendor support.
Confirm whether you can amend or cancel submissions, how approvals work for amendments, and whether the provider prevents duplicate execution. Also confirm what reports will show for amended records.
Clarify which exceptions are resolved by your team (e.g., correcting beneficiary bank details) versus those resolved by the supplier (e.g., platform-side validation failures). Document escalation paths and turnaround expectations.
Ask whether the provider can export audit-friendly evidence such as payment reference mappings, approval logs, and reconciliation reports. Confirm retention and export formats.
In payroll workflows, staff changes happen. Confirm how quickly access can be modified, whether you support automated provisioning, and how audit trails remain consistent across user lifecycle events.
For example, if some payments pass validation and others fail, clarify whether the provider executes only validated items or whether execution is blocked entirely. Ensure you understand how reconciliation distinguishes successful and failed items.
When evaluating payment and payroll-adjacent services, it’s prudent to benchmark expectations against widely used frameworks. For example, general cybersecurity and governance principles are often aligned with recognized standards and publications such as the UK National Cyber Security Centre (NCSC) guidance and the ISO/IEC 27001 family. For financial market operations, settlement and payment reliability expectations typically align with regulatory and industry practice published by relevant authorities. You should always rely on documentation provided by the exact supplier contract and service description for Cloudpay IE specifics.
Note: This article intentionally avoids claiming specific quantitative performance figures (such as cost reductions, processing times, or error rates) because those values vary by contract scope, employee volume, system integration maturity, and operational governance.
A well-run evaluation of Cloudpay IE is less about marketing claims and more about operational fit. Start with the written scope and price information, map responsibilities between your team and the supplier, validate reporting and reconciliation needs, and confirm the conditions/requirements that define onboarding success. If you follow the step-by-step approach above, you’ll reduce implementation friction and make a decision grounded in controllable evidence rather than assumptions.
To make the decision durable, ensure your internal teams participate in the evaluation: HR for inputs, Finance for reconciliation, Operations for cut-off controls, and IT for integration governance. When those stakeholders align early, your Cloudpay IE assessment becomes a process design exercise rather than a procurement checklist—leading to a smoother go-live and a more reliable ongoing payment workflow.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
4rkojvsx Technology: Industry Insights and Buying Guide
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
Mastering eCommerce with Vtex and Salesforce
This article delves into the powerful combination of Vtex and Salesforce in modern eCommerce, highlighting their roles in revolutionizing online business infrastructure. Vtex, a cloud-based platform, and Salesforce, known for customer relationship management, together provide an integrated solution for holistic business growth and enhanced customer experiences.
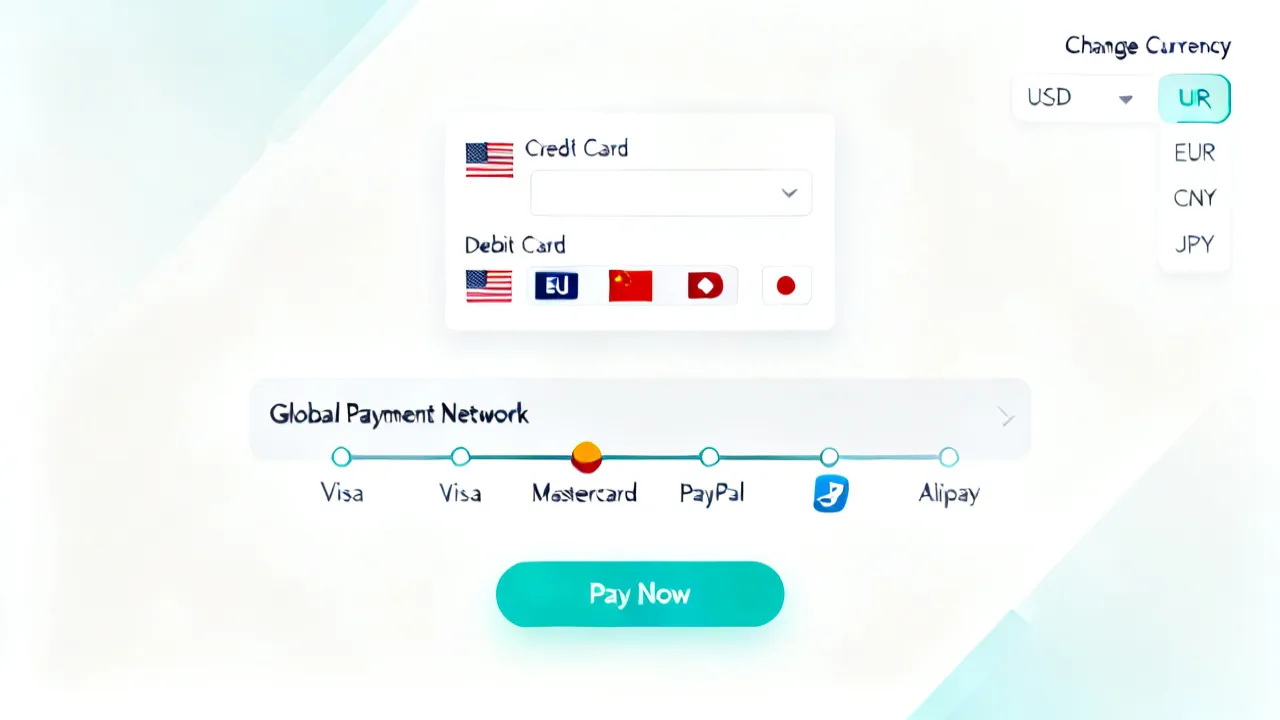
Navigating Paylane.com Payment Solutions
This guide explores the comprehensive suite of payment solutions offered by Paylane.com, focusing on their application in e-commerce and digital transactions. Paylane.com is a merchant services company that specializes in enabling businesses to process online payments efficiently. With a focus on security and adaptability, it caters to various global markets by providing tailored payment solutions.
Enhancing Business with Vtex and Salesforce
This article delves into the strategic utilization of Vtex and Salesforce in modern business operations. Vtex, known for its robust e-commerce ecosystem, and Salesforce, the paramount CRM platform, together offer an unparalleled synergy for digital commerce and customer relationship management, facilitating an integrated approach to enhance business efficiency and customer satisfaction.
Enhancing Retail with Vtex Store
Vtex Store provides a sophisticated e-commerce platform with features essential for modern retail. As a leader in the industry, it offers solutions that integrate seamlessly with business operations, enhancing both customer engagement and sales efficiency. This article explores the intricate dynamics of Vtex Store, providing insight for businesses aiming to elevate their digital footprint.
Leveraging Klaviyo Woocommerce for E-commerce Success
The integration of Klaviyo with WooCommerce presents a powerful opportunity for e-commerce businesses aiming to enhance their marketing strategies. Klaviyo, a leading email marketing platform, complements WooCommerce's robust e-commerce functionalities, creating a seamless channel for businesses to manage customer relationships and drive sales effectively. Discover how this dynamic duo can transform your e-commerce approach.
Multishop Guide for Efficient Multivendor Selling
Multishop helps businesses coordinate multivendor listings, inventory signals, and fulfillment workflows in one operational approach. This guide explains what Multishop typically means in practical commerce, how its marketplace logic relates to suppliers and pricing strategy, and what conditions companies should verify before adopting a multivendor setup.